SOC 2 Compliance Consulting
Meet Your SOC 2 Compliance Requirements
We work with organizations in critical sectors and various infrastructure nationwide to interface with SOC auditors, aid in preparation for audits, and maintain readiness between audits. Our information risk and cybersecurity services align your internal process and leadership's expectations with SOC requirements.

SOC 1 Report
SOC 1 reports focus on Internal Controls over Financial Reporting (ICFR). They are designed for service organizations whose services could impact a client's financial statements. These reports evaluate how well the organization's controls support the accuracy and integrity of financial data processing, making them essential for entities like payroll processes, claims administrators, and financial transaction handlers.
The purpose of a SOC 1 report is to provide assurance to the user entity's financial auditors that the service organization's controls are suitably designed (Type 1) and, in some cases, operating effectively over time (Type 2). This helps reduce the scope of financial audits for clients and ensures that outsourced services do not compromise financial reporting accuracy.
SOC 1 reports are primarily used by financial auditors, CFOs, and accounting teams of client organizations. These stakeholders rely on SOC 1 reports to assess the reliability of financial dat processes by third-party vendors and to support their own internal and external audit requirements.
Community
The BorderHawk Community, composed of security and compliance professional, offers strategic value to leadership and risk management teams. Within the community, leaders gain access to real-time insights on emerging threats, regulatory updates, and proven mitigation strategies - shared by BorderHawk experts and peers who face similar challenges.
This collective intelligence accelerates decision-making, enhances incident response readiness, and fosters a culture of continuous improvement. For compliance officers and CISOs, the ability to benchmark practices, validate interpretations of complex regulations, and source solutions to nuanced problems reduces isolation and increases confidence in their programs.
Ultimately, the BorderHawk community strengthens organizational resilience and ensures that security and compliance efforts are both proactive and aligned with industry best practices.
Risk Assessment
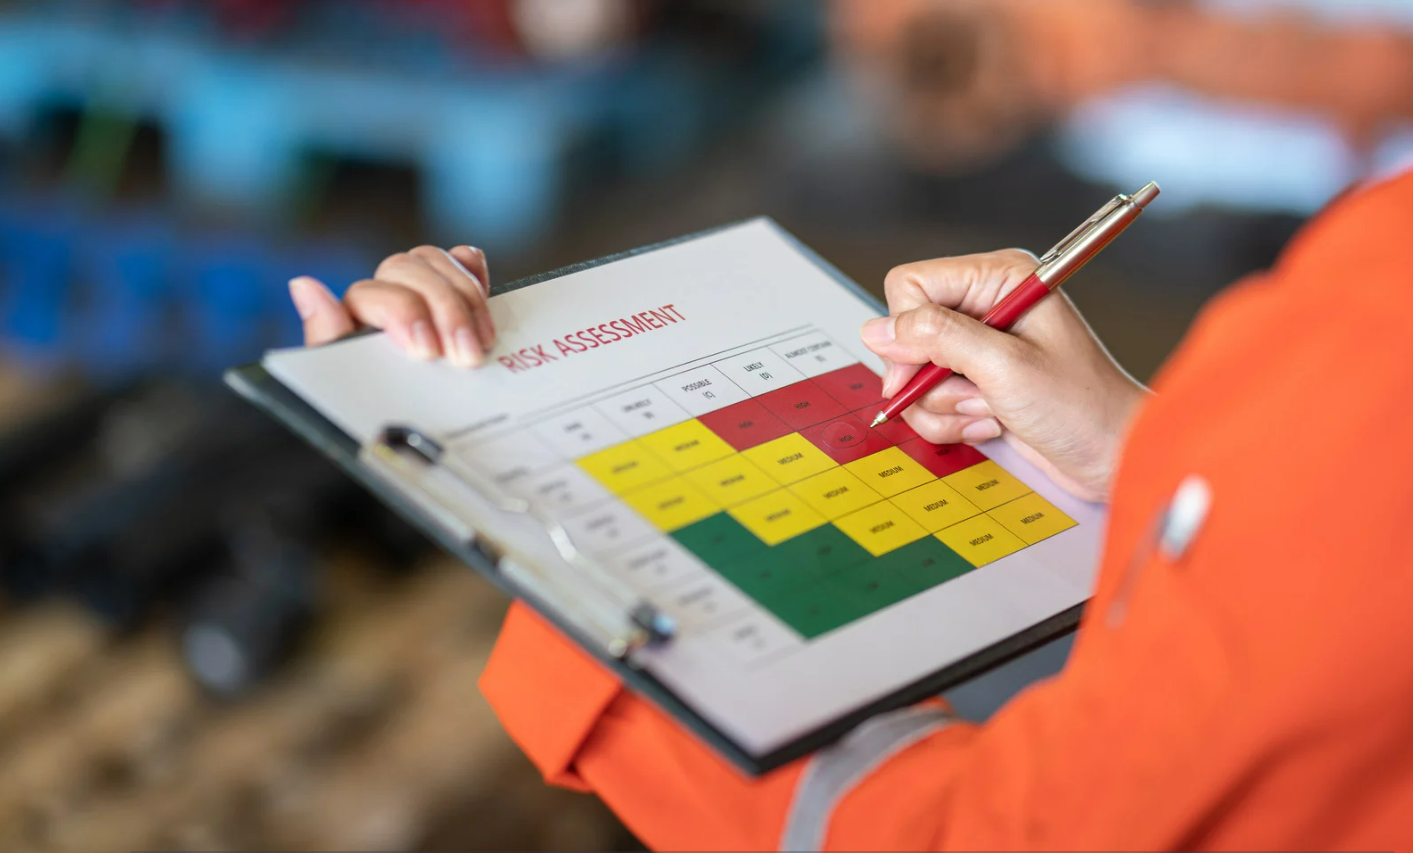
Risk assessments are essential for any organization aiming to maintain strong security and compliance postures. They provide a structured approach to identifying vulnerabilities, evaluating potential threats, and understanding the impact of security incidents on sensitive information.
By regularly conducting risk assessments, organizations can prioritize resources effectively, implement targeted safeguards, and demonstrate due diligence in meeting their regulatory, contractual, and internal requirements. Risk assessments not only reduce the likelihood of data breaches and compliance violations, but also build trust with patients, partners, and regulators by showing a proactive commitment to protecting sensitive information.
In a rapidly evolving threat landscape, risk assessments are not just a regulatory checkbox - they are a strategic necessity.
Overwatch Compliance Framework
A detailed compliance framework is critical for organization to navigate the complex landscape of regulatory and contractual mandates. Such a framework provides a structured, repeatable approach to managing policies, processes, incident response, and security controls - ensuring that every aspect of compliance is addressed systematically.
The rigor the Overwatch Framework brings helps eliminate gaps, reduce human error, and align internal practices with external expectations. Moreover, a well-documented framework enhances accountability, simplifies audits, and enables faster adaptation to regulatory changes.
The Overwatch Framework transforms compliance from a reactive obligation into a proactive, strategic asset that supports operational excellence and builds stakeholder trust.