PCI DSS Compliance Consulting
Meet Your PCI-DSS Compliance Requirements
We work with organizations that accept, transmit, and store cardholder data (payment card information) to build cardholder environments, assess those environments, and validate attestations of compliance. Our information risk and cybersecurity services align your internal processes and leadership's expectations with PCI requirements.
PCI-DSS Requirements
The Payment Card Industry Data Security Standard (PCI DSS) is a globally recognized framework developed by the PCI Security Standards Council to protect cardholder data and ensure secure payment processing. It was established by major credit card brands - Visa, MasterCard, American Express, Discover, and JCB - to create a unified standard for organizations that store, process, or transmit payment card information. PCI DSS outlines a set of technical and operational requirements designed to safeguard sensitive data, reduce fraud, and maintain trust in the electronic payment ecosystem.
PCI DSS applies to all entities involved in payment card processing, including merchants, financial institutions, point-of-sale vendors, and service providers. The standard is structured around 12 core requirements grouped into six overarching goals, such as building secure networks, protecting stored cardholder data, maintaining a vulnerability management program, and implementing strong access control measures. Compliance with PCI DSS is not optional - any organization that handles payment card data must adhere to its requirements to avoid penalties, data breaches, and reputational damage.
Payment Card Information
Payment card information, also known as cardholder data, includes the primary account number (PAN) and may also include the cardholder's name, expiration date, and service code. In some cases, sensitive authentication data - such as full magnetic stripe data, CVV codes, and PINs - may also be involved, though this data must never be stored after authorization. PCI DSS is specifically designed to protect this information during storage, processing, and transmission, ensuring that it is encrypted, access-controlled, and monitored to prevent unauthorized use or theft.
Compliance Requirements
How We Can Help You
Community
The BorderHawk Community, composed of security and compliance professional, offers strategic value to leadership and risk management teams. Within the community, leaders gain access to real-time insights on emerging threats, regulatory updates, and proven mitigation strategies - shared by BorderHawk experts and peers who face similar challenges.
This collective intelligence accelerates decision-making, enhances incident response readiness, and fosters a culture of continuous improvement. For compliance officers and CISOs, the ability to benchmark practices, validate interpretations of complex regulations, and source solutions to nuanced problems reduces isolation and increases confidence in their programs.
Ultimately, the BorderHawk community strengthens organizational resilience and ensures that security and compliance efforts are both proactive and aligned with industry best practices.
Risk Assessment
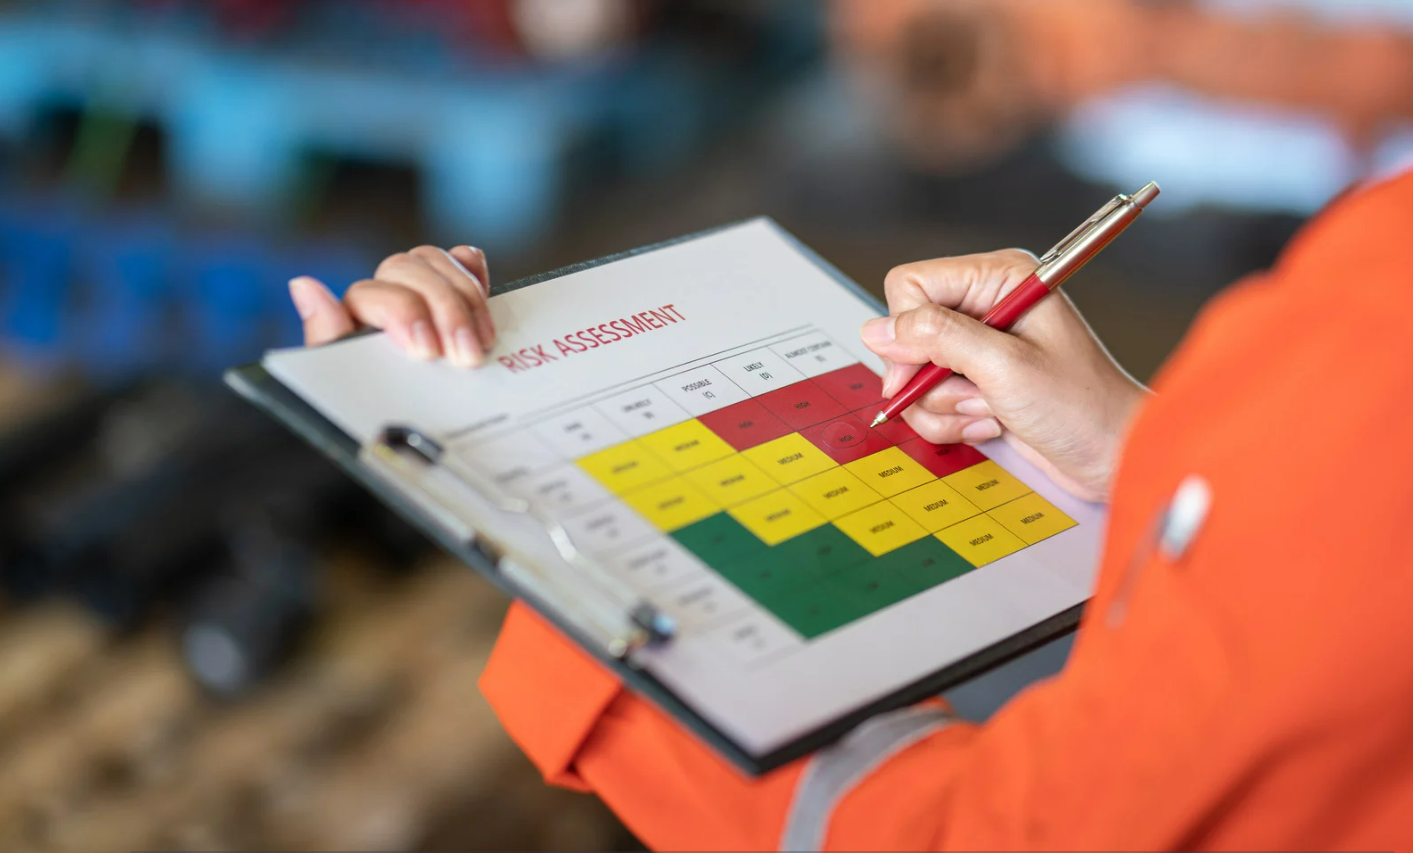
Risk assessments are essential for any organization aiming to maintain strong security and compliance postures. They provide a structured approach to identifying vulnerabilities, evaluating potential threats, and understanding the impact of security incidents on sensitive information.
By regularly conducting risk assessments, organizations can prioritize resources effectively, implement targeted safeguards, and demonstrate due diligence in meeting their regulatory, contractual, and internal requirements. Risk assessments not only reduce the likelihood of data breaches and compliance violations, but also build trust with patients, partners, and regulators by showing a proactive commitment to protecting sensitive information.
In a rapidly evolving threat landscape, risk assessments are not just a regulatory checkbox - they are a strategic necessity.
Overwatch Compliance Framework
A detailed compliance framework is critical for organization to navigate the complex landscape of regulatory and contractual mandates. Such a framework provides a structured, repeatable approach to managing policies, processes, incident response, and security controls - ensuring that every aspect of compliance is addressed systematically.
The rigor the Overwatch Framework brings helps eliminate gaps, reduce human error, and align internal practices with external expectations. Moreover, a well-documented framework enhances accountability, simplifies audits, and enables faster adaptation to regulatory changes.
The Overwatch Framework transforms compliance from a reactive obligation into a proactive, strategic asset that supports operational excellence and builds stakeholder trust.
FAQs
-
What is a PCI DSS SAQ and which one applies to us?
A Self-Assessment Questionnaire (SAQ) is the streamlined form merchants use to attest to PCI DSS compliance; which of the several SAQ types applies depends on how you accept, process, and store cardholder data — BorderHawk helps determine the correct one for your environment.
-
What's the difference between an SAQ and a full PCI DSS Report on Compliance (ROC)?
An SAQ is a self-assessment available to smaller or lower-risk merchants; a ROC is a full assessment conducted by a Qualified Security Assessor (QSA), generally required for higher transaction volumes or more complex cardholder data environments.
-
What is a Cardholder Data Environment (CDE) and why does scoping it matter?
The CDE is the set of systems, people, and processes that store, process, or transmit cardholder data; correctly scoping the CDE is the single biggest driver of PCI DSS cost and effort, since it determines exactly which requirements apply.
-
Can outsourcing payment processing reduce our PCI DSS scope?
Yes — merchants that fully outsource payment processing to a PCI DSS-compliant vendor (through a redirect or hosted iframe) can often qualify for the shortest SAQ (SAQ A), significantly reducing their compliance burden
-
How often do we need to complete a PCI DSS assessment?
PCI DSS compliance validation, whether via SAQ or ROC, is required annually, along with quarterly vulnerability scans for most merchant levels.
-
What's an Attestation of Compliance (AOC)?
The AOC is the formal document submitted alongside your SAQ or ROC confirming the accuracy of your responses and your current PCI DSS compliance status, typically required by your acquiring bank or payment brand.
-
Does PCI DSS apply to us if we only take a small number of card payments?
Yes — PCI DSS applies to any merchant that accepts, processes, stores, or transmits cardholder data, regardless of transaction volume, though lower-volume merchants generally qualify for a simpler SAQ.
-
What's the difference between a merchant and a service provider under PCI DSS?
A merchant accepts payment cards for goods or services; a service provider is directly involved in processing, storing, or transmitting cardholder data on behalf of another entity — service providers face additional requirements and must use SAQ D Service Provider if self-assessing.
-
What happens if we store cardholder data on our own systems?
Storing cardholder data on your own premises generally disqualifies you from the simpler SAQ types and requires a more comprehensive assessment (typically SAQ D), since it significantly expands your compliance scope.
-
How does BorderHawk help beyond just completing the paperwork?
BorderHawk helps you scope your CDE correctly, identify and remediate control gaps before your assessment, and complete the appropriate SAQ or prepare supporting documentation for a QSA-led ROC — reducing both compliance cost and audit risk.